#gitlabsecurity - Beeble Blog
Cyber Security
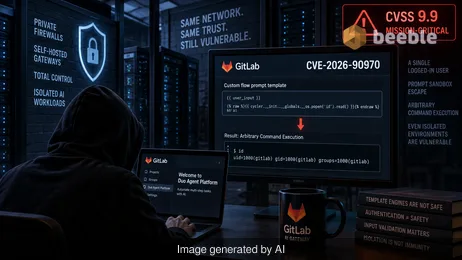
GitLab issued a critical patch for CVE-2026-90970, a 9.9 CVSS flaw in the AI Gateway. Learn how to secure your self-hosted server from command execution.
Alexey Drobyshev
October 5, 2026
Cyber Security
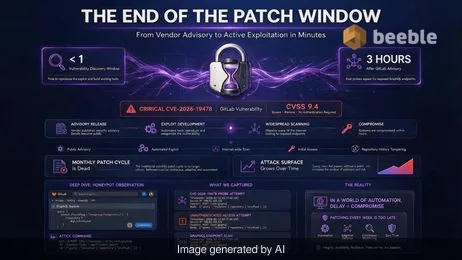
GitLab CVE-2026-19478 allows unauthenticated attackers to modify or delete projects. Learn how to defend against this AI-accelerated code injection flaw.
Alexey Drobyshev
August 21, 2026
See you on the other side.
Our end-to-end encrypted email and cloud storage solution provides the most powerful means of secure data exchange, ensuring the safety and privacy of your data.
/ Create a free accountCustom domains
Up to 1 TB storage
Advanced sharing
End-To-End Encryption
Self-destructing emails
Custom domains
Up to 1 TB storage
Advanced sharing
End-To-End Encryption
Self-destructing emails

