Cyber Security
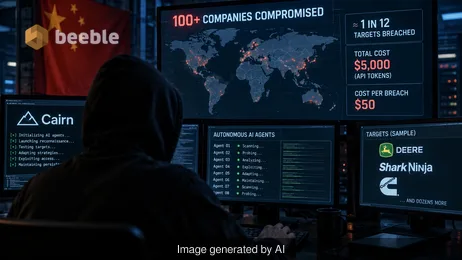
An autopsy of how a hacker used AI agents and $5,000 to breach 100+ companies, including Deere and Cummins, for just $50 per successful intrusion.
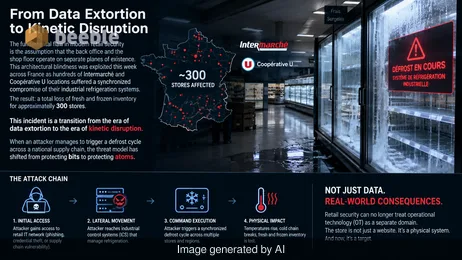
Analysis of the French supermarket refrigeration cyberattack, focusing on OT/IT convergence, architectural failure, and retail supply chain risks.
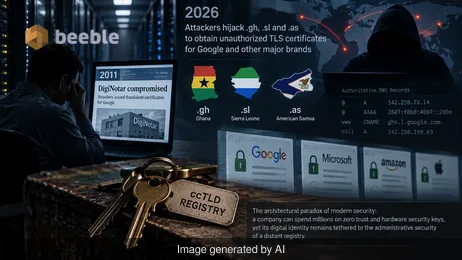
Attackers hijacked .gh, .sl, and .as country code top-level domains to issue unauthorized TLS certificates for Google and other global brands.
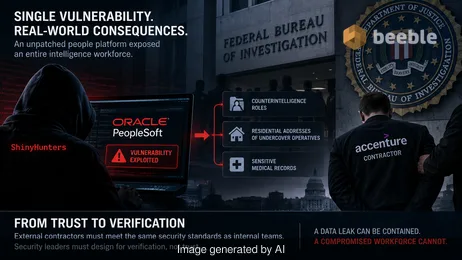
Analysis of the FBI breach involving Accenture and Oracle PeopleSoft. Strategies for mitigating third-party risk and implementing microsegmentation.
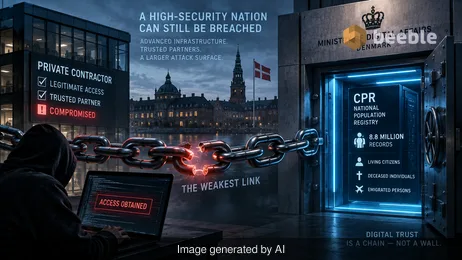
Analysis of the 2026 Denmark CPR breach affecting 8.8 million people through a third-party vendor. Learn how supply chain risks impact national security.
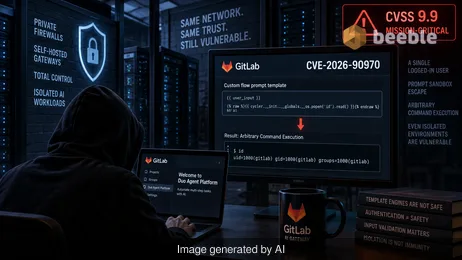
GitLab issued a critical patch for CVE-2026-90970, a 9.9 CVSS flaw in the AI Gateway. Learn how to secure your self-hosted server from command execution.
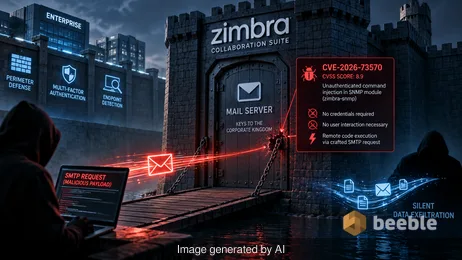
An analysis of CVE-2026-73570, an unauthenticated command injection flaw in Zimbra Collaboration Suite exploited to deploy web shells and steal credentials.
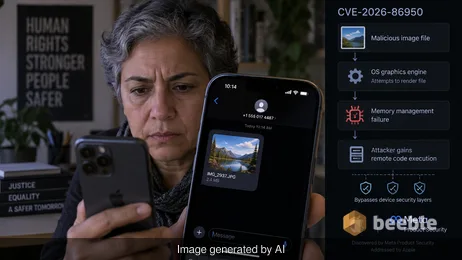
Apple patches CVE-2026-86950, a CoreGraphics flaw exploited in targeted attacks. Learn how this out-of-bounds write affects iOS and macOS devices.
See you on the other side.
Our end-to-end encrypted email and cloud storage solution provides the most powerful means of secure data exchange, ensuring the safety and privacy of your data.
/ Create a free account
